
Email and integrations
How to send your workspace's outbound email from your own domain with a Resend key, what happens until you do, and what else lives on the Integrations settings page.
Browse documentation
Mail your agents send should come from you
Email your workspace sends through Nagent, from its agents and workflows, goes out through an email service. Until you add your own account, Nagent sends it through a shared Nagent account, and recipients see a Nagent address as the sender. That is fine for trying things out. For anything a customer of yours will read, you want it to come from your own domain.
Email to prospects, people who have never written to you, is the exception: it never goes through the shared Nagent account. NORA sends it from a team member's own mailbox, your Instantly or Smartlead campaign, or your own Resend key. Until one of them is set up, her prospect emails are refused at send time and the drafts stay in Review. See cold email from NORA.
The Integrations page in Settings is where you set that up. Go to Settings, then Integrations, or open nagent.ai/admin/settings/integrations.
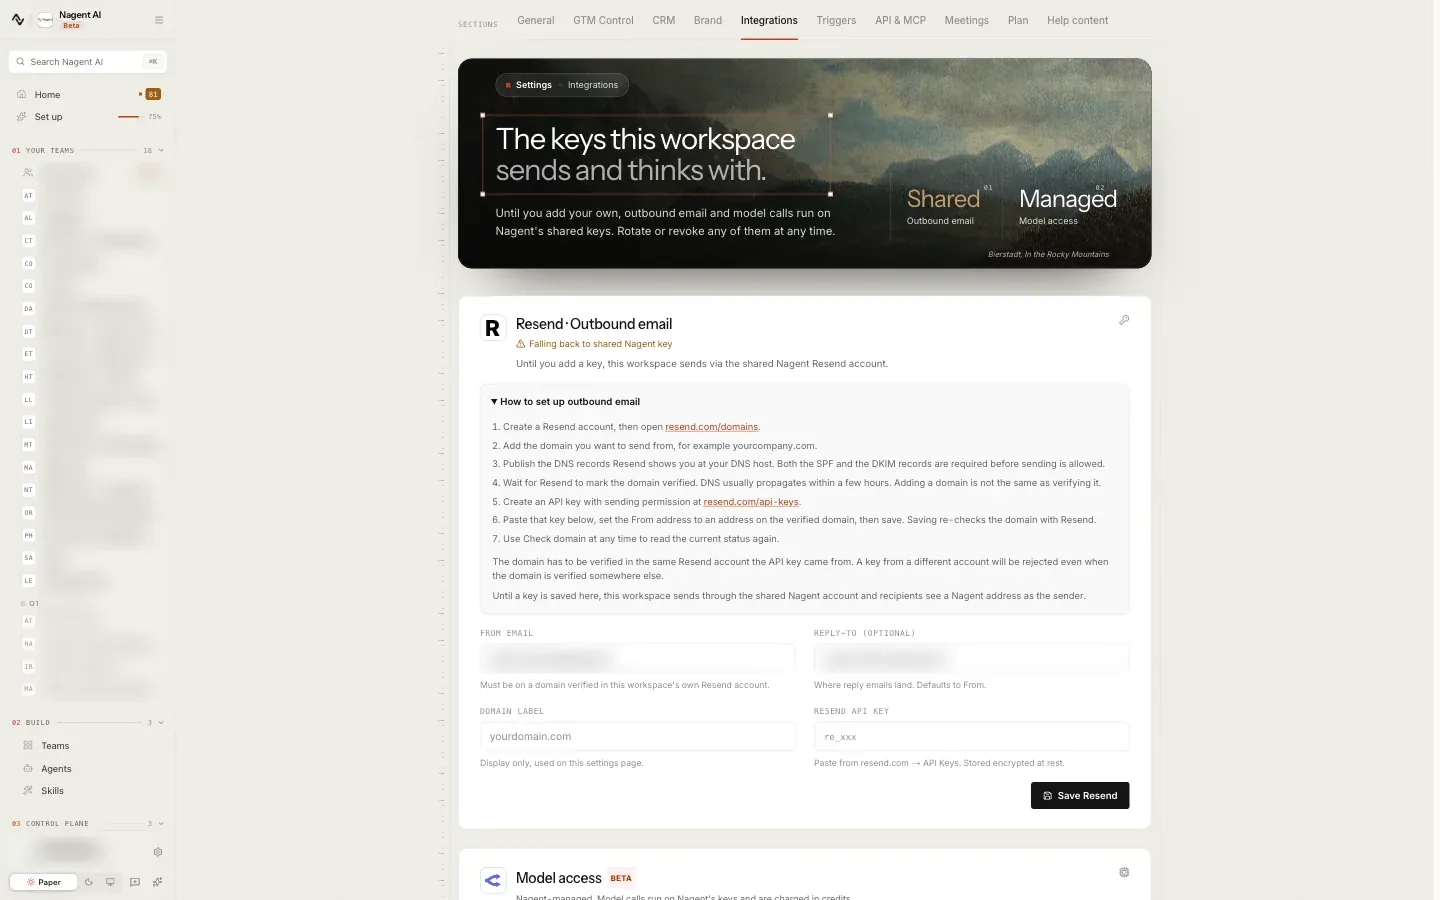
The outbound email card
The card is titled Resend · Outbound email. Resend is the email service Nagent sends through, and you bring your own Resend account.
Under the title, the card tells you where you stand:
- Falling back to shared Nagent key: no key is saved. "Until you add a key, this workspace sends via the shared Nagent Resend account."
- Workspace key configured, with the last characters of the key: your own account is in use.
Setting up your own sending domain
The card opens a guide, How to set up outbound email, until a key is saved. The steps, as the page gives them:
- Create a Resend account, then open resend.com/domains.
- Add the domain you want to send from, for example
promptworld.example. - Publish the DNS records Resend shows you at your DNS host. Both the SPF and the DKIM records are required before sending is allowed.
- Wait for Resend to mark the domain verified. DNS usually propagates within a few hours. Adding a domain is not the same as verifying it.
- Create an API key with sending permission at resend.com/api-keys.
- Paste that key into the card, set the From address to an address on the verified domain, then save. Saving re-checks the domain with Resend.
- Use Check domain at any time to read the current status again.
One rule catches people out: the domain has to be verified in the same Resend account the key came from. A key from a different account is rejected even when the domain is verified somewhere else.
The fields
| Field | What to put in it |
|---|---|
| From email | The sender address, on your verified domain. For example hello@promptworld.example |
| Reply-To | Optional. Where replies land. Defaults to the From address |
| Domain label | Display only, shown on this page |
| Resend API key | The key from step 5. It starts re_ |
Select Save Resend. The page confirms the save and shows the result of the domain check.
Reading the domain status
After a save or a check, a line under the title says what Resend reported:
| Status | What it means |
|---|---|
| Verified | The domain can send |
| Pending | Added to Resend, DNS still propagating |
| Not started | Added, but verification has not been started in Resend |
| Failed | The DNS records are missing or wrong |
| Partially verified or partially failed | At least one record is not right yet, so sending is not enabled |
| Sending disabled | Verified, but sending is switched off on it in Resend |
| Not found | The domain is not in the Resend account this key belongs to |
| Check failed | The check did not complete; the key may be revoked or from another account |
The line also says when the domain was last checked.
Changing or removing the key
To rotate the key, paste a new one and save. Remove key deletes it, and the workspace goes back to the shared Nagent account straight away.
Our logic
Mail from an unverified domain lands in spam or is refused, and mail from someone else's domain misleads the person who reads it. So the page checks the domain against the account behind your key every time you save, and says plainly what is wrong instead of letting sends fail silently later.
The key is stored encrypted, and the page only ever shows a masked hint of it.
Bounces and complaints on your own key
NORA's prospect emails sent on your own key report their bounces and spam complaints to your Resend account, not ours. To pass them on:
- In your Resend account, add a webhook to
https://nagent.ai/api/webhooks/resendfor email.bounced and email.complained. - Copy the webhook's signing secret, which starts with
whsec_. - Paste it into Webhook signing secret on the outbound email card and save.
From then on a hard bounce or a complaint writes the address to your suppression list, as it does on every other sender. The secret is stored encrypted and is used only for events on NORA's prospect emails from this workspace.
Cold email from NORA (Beta)
NORA's prospect email leaves through one of three senders, chosen in NORA, Settings, Controls, under Cold email sender:
- Team members' own mailboxes. Each member connects Gmail or Outlook under Settings, CRM, Your sending account, and you tick the ones NORA may send from. She rotates across them, keeps each one under a daily cap that warms up over 21 days, and reads replies back from the same mailbox.
- Instantly or Smartlead. Connect the tool on the Integrations page: paste the API key (it is checked with the tool before it is saved), pick the campaign, and add the webhook shown on the card. NORA adds each approved email to the campaign as a lead and the tool sends it.
- Your own Resend key, the card above. Resend's terms do not allow cold outreach, so this is the last choice and the card says so.
Setting up the Instantly or Smartlead campaign
Do this once in the tool, for the campaign NORA uses:
- Make the campaign a single step.
- Set the step's subject to
{{nora_subject}}and its body to{{nora_body}}. NORA's subject and body, with the unsubscribe link and your postal address already in the footer, arrive in those two fields. - Add a webhook to the URL shown on the Nagent card, for replies, bounces and unsubscribes. In Instantly these events are reply_received, email_bounced and lead_unsubscribed; in Smartlead they are EMAIL_REPLY, EMAIL_BOUNCE and LEAD_UNSUBSCRIBED. Instantly webhooks need its Hyper Growth plan or above.
The secret in the webhook URL is how an event finds your workspace, so treat the URL like a password. New webhook URL replaces it, and the old one stops working at once.
A sent draft reads "Queued in Instantly" (or Smartlead). The tool sends on the campaign's schedule, so NORA does not claim it was delivered.
Your own mailbox for CRM email (Beta)
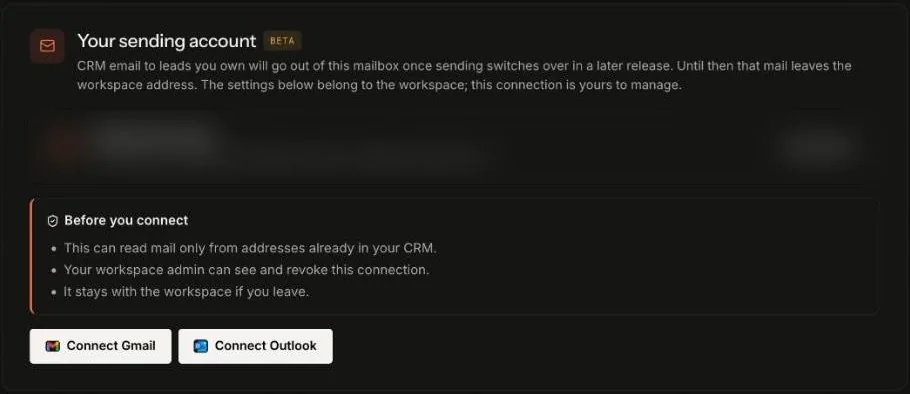
Separately from the workspace sender, each person on your team can connect their own mailbox for CRM email to the leads they own. That lives on Settings, CRM, under Your sending account, with Gmail and Outlook offered. It is marked Beta. Once a mailbox is connected, the card reads "Connected and sending.", and approved agent follow-ups to a lead go out from the mailbox of the person who owns that lead. A lead with no owner, or an owner with no mailbox, uses the workspace address, which is the one you set up above. The CRM guide covers what else changes.
Tool keys
The page's subtitle mentions keys for agent tool execution, but there is no tool key field on it today. Every workspace uses the shared Nagent account for tool execution. Your own tool connections, such as your CRM, calendar or email, are authorised under your workspace when you connect them, and nobody else's workspace can use them. Connect tools from Connect your tools; see Third-party tools and Tools and integrations.
Model access (Beta)
The second card, Model access, says whose key your agents' model calls use. Under Whose key model calls use there are two choices.
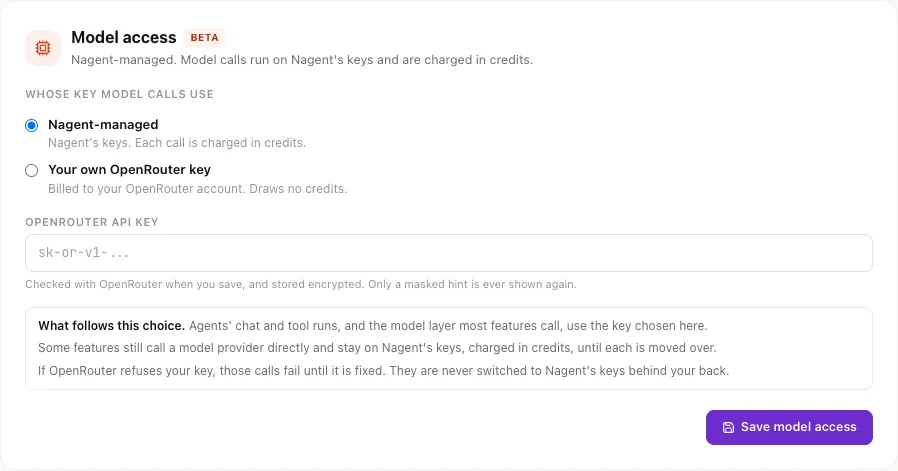
| Choice | Who pays |
|---|---|
| Nagent-managed | Model calls run on Nagent's keys and each call is charged in credits. The default |
| Your own OpenRouter key | Calls are billed to your own account with that provider and draw no credits |
Using your own key is part of the Enterprise plan; on other plans the second choice is shown but cannot be picked, and the card says so. Your key is checked when you select Save model access, stored encrypted, and only a masked hint of it is shown again.
The card is plain about the limits. Agents' chat and tool runs, and the model layer most features call, use the key you choose. Some features still call a model provider directly and stay on Nagent's keys, charged in credits, until each is moved over. If your key is refused, those calls fail until it is fixed; they are never switched to Nagent's keys behind your back.
The site connection (Beta)
The third card, Site connection, issues the key your own website uses to read the fixes you approve on the Proposals page. The key is shown once, when it is issued; after that only its last four characters exist anywhere. You can rotate or revoke it. The card cannot see whether your site is actually reading the key, so it says so rather than claiming a connection. The developer steps are in Connect your site.
WordPress (Beta)
The WordPress card sends each article you approve to your own WordPress site as a draft. You connect it with the site address, a WordPress username and an application password, not with the site key above. Your editors publish the draft from WordPress; Nagent never publishes there. The steps are in send approved articles to WordPress.
Who can do this
Anyone with settings read permission can open the page. Saving or removing a key, checking the domain, and issuing the site key need settings write permission, which a workspace admin has.
Where to go next
- Triggers and webhooks: let outside services start work in your workspace.
- Third-party tools: connect a tool and choose what agents may do with it.
- Connect your site: put approved fixes on your website.