
People and roles
How to invite a teammate with a role at the whole organisation, a department or a team, what each of the five roles may do, how to grant and remove roles, and how to reset a password or deactivate someone.
Browse documentation
Agents do the work, people decide it
A workspace runs with one person in it, but it is designed for several. Agents need someone to approve what they send, someone to connect the tools they act in, and someone to set the money they may spend. Those are jobs for people, and the role you give each person decides which of them they can do.
People are managed on Team Members. Only an Organisation admin can invite, grant roles, reset passwords or deactivate. A Chief of staff sees the list read-only, and the other roles do not see the page.
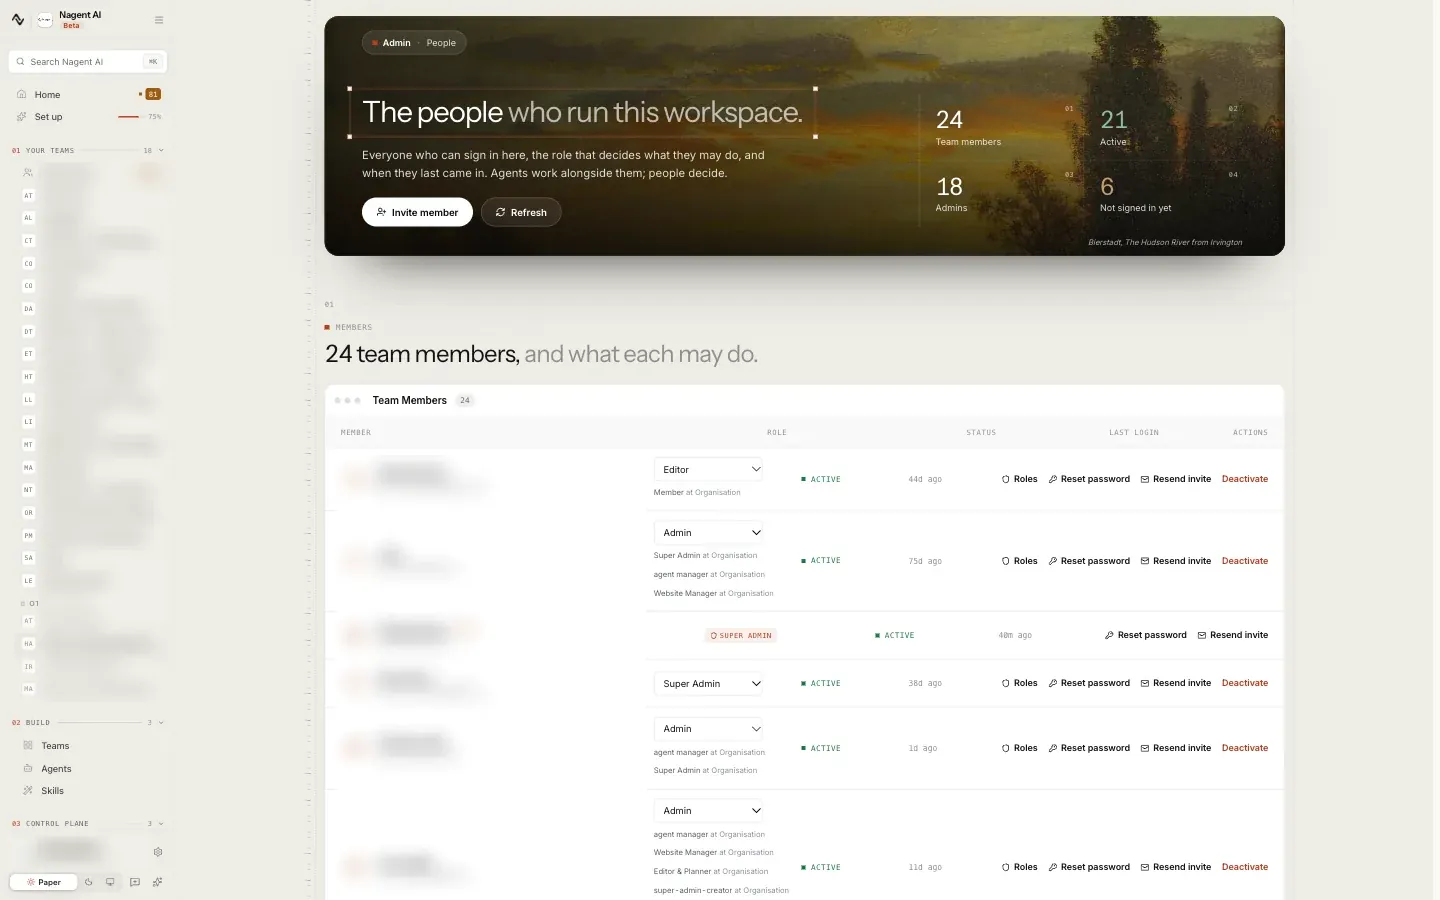
The list shows each person's name and e-mail, their Role, their Status (Active or Inactive) and their Last login. Under the role, each row lists the roles the person holds and where, for example "Member at Organisation". Those are what decide what they may do.
Inviting a teammate
- Open Team Members and press Invite member.
- Fill in Name and Email.
- Choose a Role. It defaults to Member, so check it. Each role shows a line under it saying what it is for.
- Under At, choose where the role applies: Whole organisation, A department or A team, then pick the department or team. A Chief of staff is always given at a department and a Team lead at a team.
- Press Send invite.
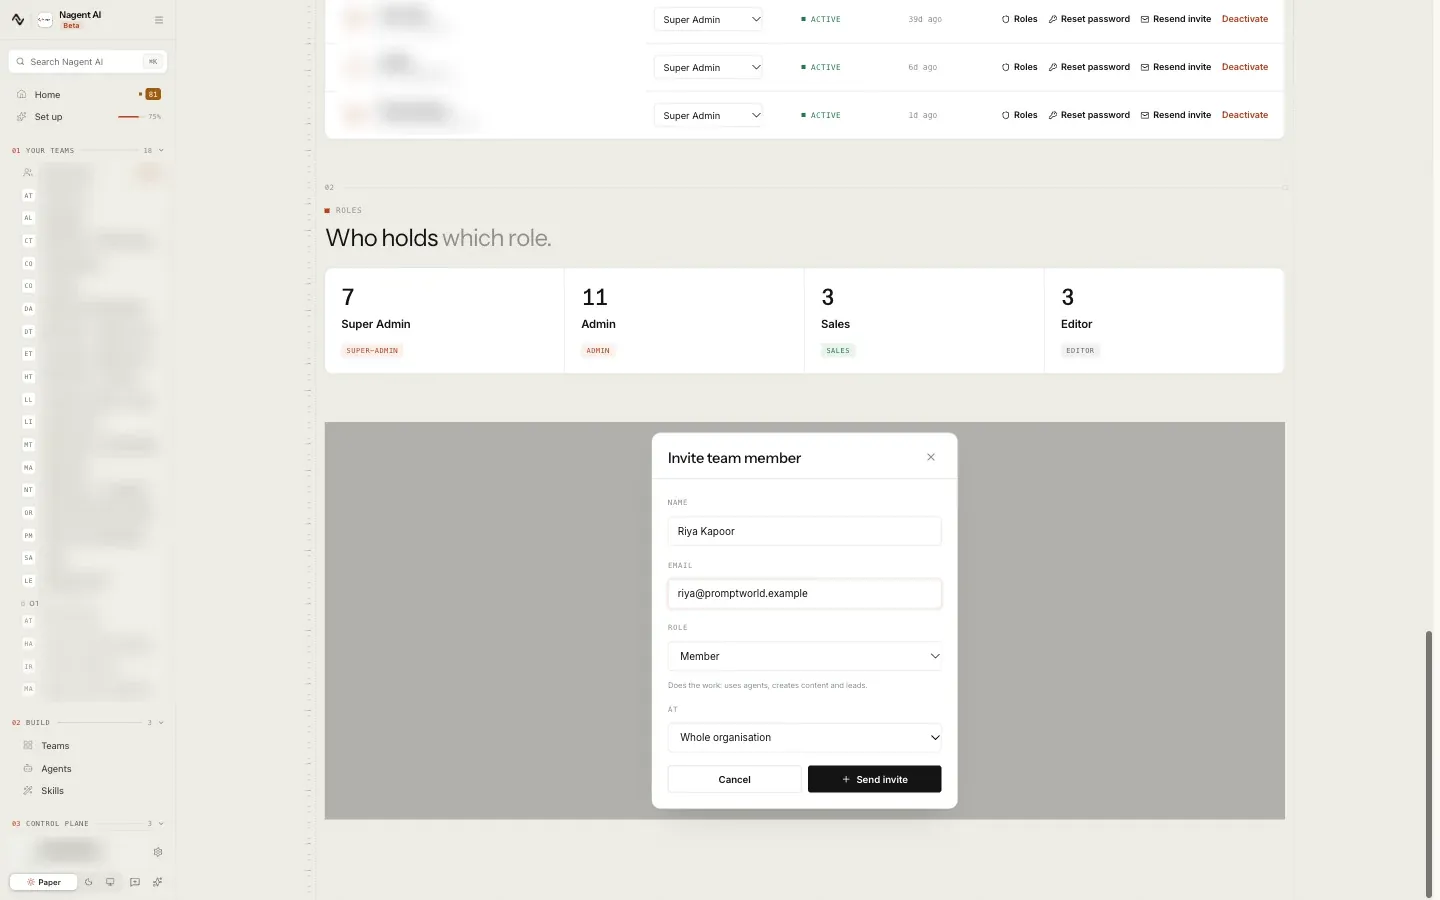
The dialog confirms "(name) has been invited" and "An email with login details was sent to (address)."
If the e-mail could not be sent, the dialog says so and shows the Temporary password with a Copy button. Pass it to your teammate yourself, over a channel you trust.
Some things to know:
- An address that already has a Nagent account cannot be invited. The invitation is refused with "A user with this email already exists".
- The new member is active immediately. They count as a person in the workspace from the moment you invite them, before they have signed in.
- The invitation does not put anyone in a room. A role at a department decides what the person may do there; it does not add them to the room's members. A room's members add them from inside the room. An Organisation admin can also join any room themselves, from Other teams in the sidebar (see the team room).
The invitation e-mail
The e-mail is headed "You're invited to the (workspace) admin panel" and names your workspace. It contains the person's e-mail, a temporary password, and a Sign in to Admin button that opens the sign-in page. It asks them to change the password after signing in.
They can also skip the temporary password and sign in with an e-mailed link or with Google. See signing in.
Resend invite in the person's row mints a new temporary password and e-mails it. The previous one stops working.
The five roles
Every role is held at a place in your organisation: the whole organisation, one department or one team. What the person may do applies there and below it, so a role at a department reaches that department and the teams inside it, and nothing else.
| Role | Held at | Who it is for |
|---|---|---|
| Organisation admin | The whole organisation | People, roles, settings: everything, across the organisation |
| Chief of staff | A department | Runs one department: its teams, agents, approvals, content and leads |
| Team lead | A team | Runs one team: approves its agents' work and edits its agents |
| Member | Anywhere | Does the work: uses agents, creates content and leads |
| Viewer | Anywhere | Reads |
A department is one of your team rooms, as listed on Teams. A team is a smaller group inside a department, set up on the Knowledge Hub's Teams tab. If you have none yet, grant the role at the whole organisation.
The person who created the workspace is an Organisation admin. You cannot change your own roles or deactivate yourself, so a workspace always keeps the admin who is looking at it.
Roles that come with Forward deployed
Three more roles are for Forward deployed engagements. An engagement gives them to the people it seats in your workspace, for the engagement's dates:
| Role | Who it is for |
|---|---|
| Deployed engineer (operate) | Runs the agent system for the workspace: set-up, agents, training and context |
| Deployed engineer (operate and build) | Runs the agent system and builds integrations, agents, products and workflows |
| Deployed manager | Runs the agent system for the engagement and owns its objectives. The only one of the three who can decide your approvals |
A deployed seat never holds secrets, people and roles, finance or payroll permissions, whatever its role.
How an engagement is approved, paused and ended is on Forward deployed.
What each role may do
This table is the permission set each role carries today, wherever it is held.
| Can they | Organisation admin | Chief of staff | Team lead | Member | Viewer |
|---|---|---|---|---|---|
| Invite people, grant roles, deactivate | Yes | No | No | No | No |
| See the Team Members list | Yes | Yes | No | No | No |
| Change settings, connect tools, set the brand | Yes | No | No | No | No |
| Create agents | Yes | No | No | No | No |
| Staff teams with agents; set an agent's level | Yes | Yes | Yes | No | No |
| Run a team's workflows | Yes | Yes | Yes | Yes | No |
| Build, change, publish and schedule workflows | Yes | Their department's | Their team's | No | No |
| See agents | Yes | Yes | Yes | Yes | Yes |
| Edit agents' set-up | Yes | Yes | Yes | Yes | No |
| Read the Knowledge Hub | Yes | Yes | Yes | Yes | Yes |
| Add to the Knowledge Hub | Yes | Yes | Yes | Yes | No |
| Read leads | Yes | Yes | Yes | Yes | Yes |
| Change leads | Yes | Yes | Yes | Yes | No |
| Change the CRM; send e-mail and proposals | Yes | Yes | Yes | No | No |
| Delete leads | Yes | No | No | No | No |
| Write content | Yes | Yes | Yes | Yes | No |
| Publish content | Yes | Yes | Yes | No | No |
| Publish campaigns and events | Yes | Yes | No | No | No |
| See approval requests | Yes | Yes | Yes | Yes | No |
| Decide approval requests | Yes | Yes | Yes | No | No |
| Read the audit log | Yes | Yes | Yes | No | No |
Publishing a workflow also needs permission to govern AI agents. See building a workflow.
A Member asks; a lead decides. Work an agent holds for a person waits in the Inbox. A Member sees it there but cannot decide it. An Organisation admin, or a Chief of staff or Team lead where the work belongs, can. If you are the only person in the workspace, you decide everything yourself; when you invite others, give at least one of them a role that can decide. See approvals and the Inbox.
The roles Home suggests are jobs, not roles. Home suggests inviting a growth lead, someone from IT or security, and someone from finance. Naming team numbers, connecting tools and setting caps all need the Organisation admin role today.
Choosing a role
For Prompt World, a team of five might look like this:
| Person | Role | At | Why |
|---|---|---|---|
| Founder | Organisation admin | Whole organisation | Runs the workspace and decides what agents send |
| Head of marketing | Chief of staff | The Marketing room | Runs marketing, its agents and its approvals |
| Sales enablement lead | Team lead | A team in the Sales room | Approves that team's agents' work |
| Account executive | Member | The Sales room | Works leads and drafts with agents |
| Workshop designer | Member | Whole organisation | Adds workshop material to the Knowledge Hub |
Start narrow. A role can be raised later in a few clicks; a role that gave too much has already been used.
Granting and removing roles
Press Roles in the person's row. Roles for the person lists each role they hold and where, each with Remove.
- Choose a Role and, under At, where it applies.
- Press Grant role. A person holds one role at each place, so granting at a place they already hold a role replaces it.
- Press Done.
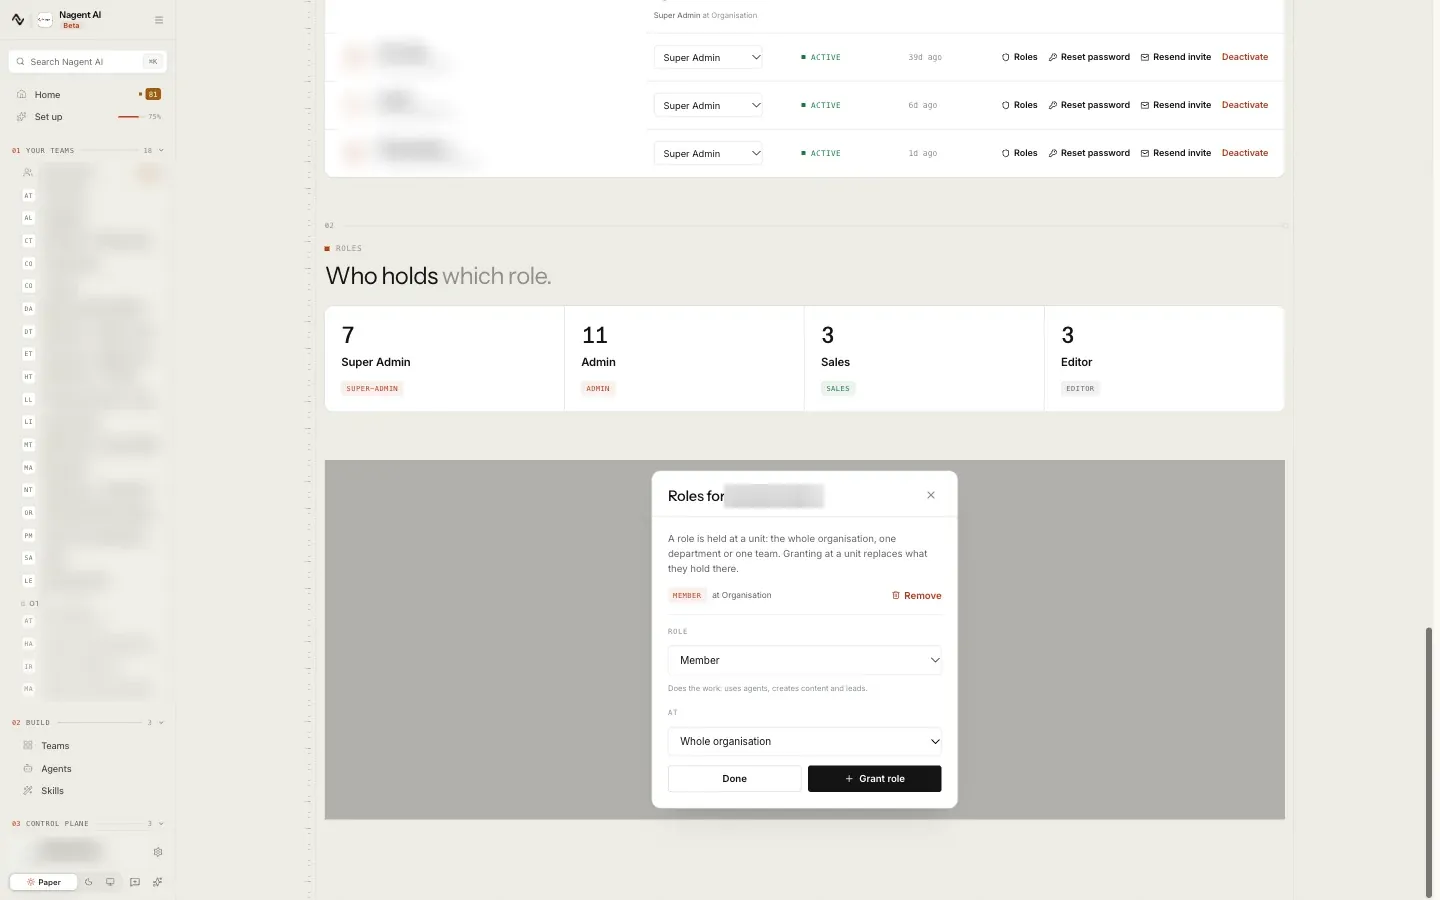
The changes apply at once. Nagent refuses a grant that would give more than you hold yourself, and says which permissions are the problem: you cannot hand out what you do not have. It also refuses changes to your own roles.
The drop-down in the Role column is the role the person holds at the whole organisation: Organisation admin, Member or Viewer. It reads "No organisation role" when they hold none there. Choosing a role in it grants that role at the whole organisation, replacing the one they held there, and the row shows the change at once. Roles at a department or a team are listed under the drop-down; change those with Roles. Someone who holds no role anywhere in the workspace has none of its permissions until you grant one.
Resetting a password
Press Reset password in the person's row and set a new password for them. It needs at least 8 characters, an uppercase letter, a lowercase letter, a number and a special character. The page confirms "Password reset for (address). Share the new password securely." Ask them to change it after signing in.
The reset ends every session the person has open, on every device, and forgets any device they asked Nagent to remember. They sign in afresh with the password you gave them. That makes Reset password the quickest way to shut someone out of a session you do not trust without deactivating them. (Resetting your own password from here keeps the session you are in.)
People can also reset their own password from Forgot password? on the sign-in page, or change it from Change password in their account menu. Either way ends their other sessions in the same manner. See signing in.
Deactivating someone
Press Deactivate in the person's row. Their status changes to Inactive and they can no longer sign in. If they connected a mailbox for sending, mail stops leaving under their name, but the mailbox and its conversations are kept, so the workspace loses no history.
Deactivating someone also revokes their personal API keys, and a workspace API key they created stops working. Create new keys if the work should go on. See the API and MCP.
Deactivation applies to the person's Nagent account, not only to your workspace. If they belong to another workspace too, they lose access there as well.
Reactivate in the same place restores sign-in and sending. It does not bring back revoked API keys.
Where to go next
- Approvals and the Inbox: what approvers see.
- Signing in: what an invited teammate does first.